One-sentence definition
Regla de diseño que concede a cada componente solo los datos y acciones mínimos necesarios durante el tiempo imprescindible.
Definition: Grant Only the Permissions Needed
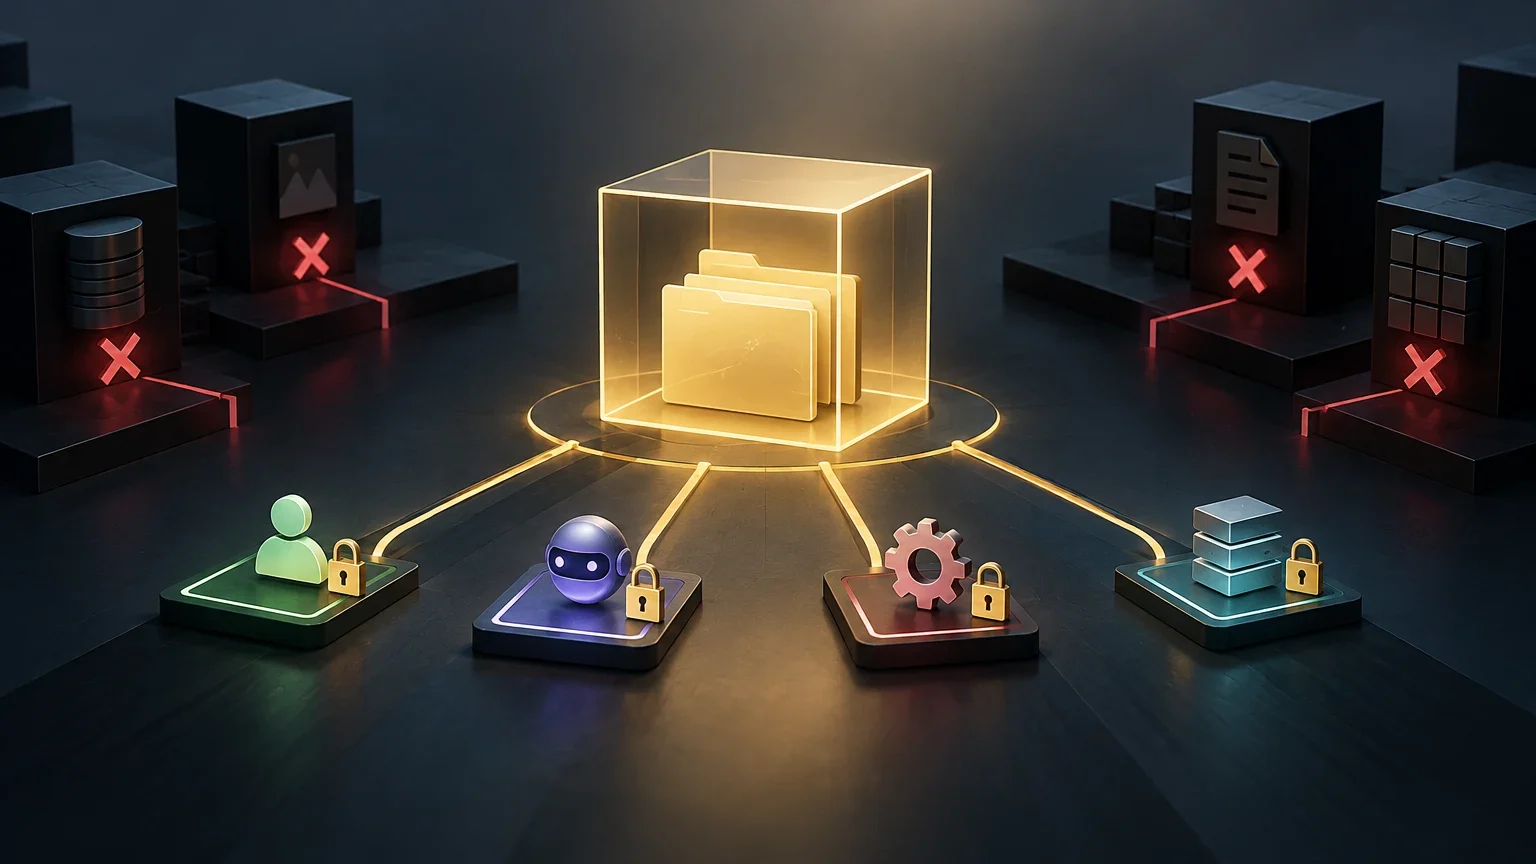
The principle of least privilege, also known as least privilege or PoLP, states that each user, process, or component should have only the permissions necessary to perform its assigned task. This applies both to the resources an identity can reach and to the operations it can perform on them. The aim is to limit the consequences of an error, misuse, or compromise of an account or process.
It does not mean that all identities should receive the same reduced permissions. Instead, each identity’s access should match its specific function. A process that needs to read a file should not be able to modify it unless that capability is necessary. A service that queries a database should not be able to administer the database server. IBM’s AIX documentation illustrates the principle at the process level and explains that restricting privileges can limit damage if an application with elevated privileges is exploited.
In an AI system, the principle applies to the identities and resources around the model: the account running the service, the agent requesting actions, the available tools, access credentials, queryable data, and network connections. This does not mean that a model has an operating-system identity of its own. That identity usually belongs to the process or service running the model, or to the component making calls on its behalf.
For more context, see the [glossary](/glossary/), the [principle of least privilege entry](/glossary/principio-menor-privilegio), and the [comparison page](/compare/).
How It Works: Identities, Permissions, and Scope
Start by identifying the components that can take action. A simple architecture might use one service identity for the backend, another to access a database, and separate credentials for an external tool. In an agent-based architecture, distinguish the model that generates a response, the orchestrator that interprets it, and the tools that perform operations. Restricting one layer does not automatically restrict the others: each permission must be enforced by the component that uses it.
Next, define the scope of authorization. Roles can group permissions for common functions; more granular controls can limit operations by resource, action, or context. For example, allowing read-only queries against a specific set of tables is not the same as granting write access to the entire database. Review permissions whenever the task, service, or sensitivity of the data changes.
Temporary privileges reduce the amount of time a capability is available. If an administrative operation is essential for a one-off task, access can be granted for a limited period and removed afterward. Time limits help narrow access, but do not authorize an operation on their own: the identity still needs to be authenticated correctly, a policy must permit the operation, and controls must prevent the credential from being used outside its intended context.
Network restrictions can also help if they limit connections to those the service needs to make. However, they are not equivalent to permissions on data or actions: a server can be isolated from the internet and still have excessive access to local files. Effective design combines complementary controls rather than assuming one barrier implements the entire principle.
Deciding Which Permissions Each Component Needs
Policies should describe specific capabilities and avoid generic privileges when access can be narrowed by resource and action.
| Component or identity | Task requirement | Narrowly scoped permission | Avoid by default |
|---|---|---|---|
| Inference process | Load the model and handle requests | Read the necessary files and use assigned resources | Run as an administrator or modify system files without a need |
| Query tool | Retrieve approved information | Read only the authorized tables or documents | Write to, delete, or administer the database |
| External connector | Send a request to a specific service | Access the required destination and operation | A broad token reusable across multiple services |
Three Examples in AI Systems
Enterprise agent with read-only database access. If an agent answers questions using internal information, the account that queries the data can be restricted to read-only access and to the necessary tables. Operations that change records should be unavailable to that identity unless an approved use case requires them. If write actions are enabled, authorize them separately and enforce checks in the service that performs them; a prompt instruction is not an access control.
Local inference server with restricted network access. A service that should accept only local connections can be configured to listen on a loopback address, such as 127.0.0.1, instead of accepting connections on every interface. This reduces which network clients can reach the port, but does not determine which files the process can read, which commands it can run, or whether another local component can call it. The listening address is an example of limiting exposure, not a complete implementation of PoLP.
AI API with narrowly scoped credentials. An application calling a provider or internal service can use a credential authorized for the required operation and resource. If the system supports temporary credentials, their lifetime can be limited; if not, scope, permissions, and revocability can be constrained according to the available features. A single-use token is not a universal requirement of the principle: claim or implement one only when the service supports it and the workflow needs it. Nor should the credential be exposed to the model if the backend can retain and use it instead.
What It Is Not: Authentication, Isolation, or Guardrails
Authentication and least privilege address different problems. Authentication checks an identity or validates credentials; authorization determines what that identity may do. Strong authentication can reduce the likelihood of an unauthorized person using an account, but it does not fix excessive permissions. Conversely, a restrictive permissions policy does not, by itself, establish who is using the account.
Network isolation or an air gap is not synonymous with PoLP either. An environment disconnected from external networks may limit certain access paths, but processes running inside it can still have more local capabilities than they need. Isolation and least privilege can complement each other: one limits communication paths or domains, while the other restricts the permissions of each identity.
Guardrails are controls intended to guide or limit inputs, outputs, and actions in an AI system. They can help reduce unwanted responses or uses, but they do not replace authorization enforced on databases, files, tools, or APIs. If a model proposes a prohibited action, the decisive control should be checked in the tool or service that performs it; do not rely solely on the model following an instruction.
Zero Trust is a broader architectural approach that includes verifying requests and controlling access. PoLP can be part of that approach by reducing the capabilities granted, but the terms are not interchangeable. Separation of duties, meanwhile, divides tasks or approvals so that one identity does not hold every relevant capability. It can coexist with least privilege, although it addresses a different risk.
Distinguishing Commonly Confused Controls
These mechanisms can work together; each controls a different dimension.
| Concept | Question it answers | Relationship to PoLP |
|---|---|---|
| Authentication | Who or what is making the request? | Identifies or validates; does not define permissions by itself |
| Authorization | Which operation is allowed on which resource? | The mechanism through which least-privilege permissions are expressed |
| Isolation | Which systems or networks can communicate? | Can reduce exposure but does not replace local permissions |
| Guardrails | Which content or actions should the AI system avoid? | Complement access policy; should not be the only barrier |
| Zero Trust | How is access verified and controlled across an architecture? | A broader approach that can include least privilege |
Operational Limits in Agents and Dynamic Systems
In a traditional system, a process’s task is often relatively well defined. An agent, by contrast, may select tools and chain steps based on the request and intermediate results. That makes it harder to determine the minimum permission set in advance, but it does not make the principle inapplicable. It means defining authorized tasks, separating capabilities, and validating each action where it is performed.
Permissions that are too broad increase the potential impact of a compromised service or an unexpected action. Permissions that are too narrow can block legitimate work, cause failures, or encourage operational shortcuts such as reusing an overprivileged account. The balance does not come from guessing a perfect configuration. It requires testing representative workflows, recording denials, understanding their causes, and adjusting permissions through review.
A model’s nondeterministic behavior does not change the definition of the principle. It does affect how safeguards should be designed: do not assume that a model will always choose the right tool or follow every instruction. Authorization should be enforced outside text generation, in the services that control data and operations. It is also useful to limit how much a single request can do, so that one mistaken decision does not automatically gain unlimited capability.
The available evidence here establishes general foundations of least privilege and examples involving process privileges, roles, and permissions. It does not directly document a universal configuration for AI agents, local inference, or AI APIs. These cases should be understood as technical applications of the principle whose feasibility depends on the specific operating system, platform, provider, and application design.
A Practical Process for Adjusting an Agent’s Permissions
Treat each adjustment as a change that can be reviewed. Do not make permissions permanent just to resolve a one-off failure.
- 01Describe the authorized task and list the data, tools, and operations it requires.
- 02Assign separate identities to components with different access needs.
- 03Start with permissions restricted by resource and action; avoid shared administrative credentials.
- 04Test successful tasks and denial cases, including attempts to access tools or data outside the task.
- 05Record authorization decisions and review whether granted permissions are still necessary.
- 06If a legitimate task fails, identify the specific missing permission and expand access only within the necessary scope and period.
Decision Criteria and Related Concepts
IAM, or identity and access management, covers practices for managing identities, authentication, and authorization. PoLP is a design principle that can be implemented through those mechanisms; it is not a product or a single technique. Role-based access control can make permissions easier to assign consistently, although a poorly designed role can grant too much. So, beyond the role’s name, check what operations it actually allows.
Separation of duties requires that certain tasks or critical stages do not depend on one person or identity. For example, one identity can prepare a change and another approve it. PoLP limits an individual identity’s capabilities; separation of duties distributes capabilities or decisions. A sound policy can combine both where the risk and workflow justify it.
When evaluating an AI integration, ask which identity makes each call, which resource it reaches, which operations it is allowed to perform, and what happens if the process behaves unexpectedly. Also check whether permissions can be revoked, whether credentials are kept out of the model’s context, and whether denials can be diagnosed without granting broad access. The answers depend on the implementation and should not be inferred from labels such as “secure agent” or “Zero Trust.”
The principle applies whenever an identity can access protected resources and its capabilities need to be limited to the intended work. The practical goal is to grant the minimum access that allows an authorized task to be completed and operated reliably, verify it in the system that performs the action, and review it when the task, data, or architecture changes.
Questions to Ask Before Approving a Permission
Use these questions to review a service account, agent tool, data connector, or API.
| Criterion | Review question | Signal to pause or investigate |
|---|---|---|
| Identity | Which component uses this permission, and does it have a distinct identity? | Multiple functions rely on one shared account without clear separation |
| Resource and action | Is access limited to the specific resource and operation? | Global permission when only read access or a subset is needed |
| Duration | Can the permission be removed when the task is complete? | Permanent elevated access for a one-off need |
| Execution | Does the service performing the action enforce authorization? | The policy relies only on instructions to the model |
| Review | Can usage be checked and the permission adjusted? | No owner, useful audit record, or revocation process |